An appointment-request form may look like a simple way to help patients contact your practice. But the information entered can travel through WordPress, the form plugin, email, hosting systems, backups, and connected services. Reviewing the full path is an important part of WordPress medical appointment request form privacy.
Before publishing or changing a form, walk through the checklist below with the person responsible for your practice’s privacy process and the person who manages your website. This is a practical review, not a substitute for guidance from your compliance or legal professionals.
Start with the purpose of the form
Decide what the form is meant to do. If its purpose is to let someone ask for a call or request a time, it may not need detailed clinical information. A focused form can ask for basic contact details and a preferred way or time to reach the person, along with any scheduling information your staff genuinely need.
Be cautious about open-ended fields that invite people to describe symptoms, medical history, medications, insurance details, or other sensitive information. If the practice has a specific reason to collect those details, have the privacy lead review the purpose and safeguards before adding the fields. A general appointment request may be better kept separate from clinical intake.
For more on this distinction, see how to think about symptom details in a website form.
Trace every place a submission can go
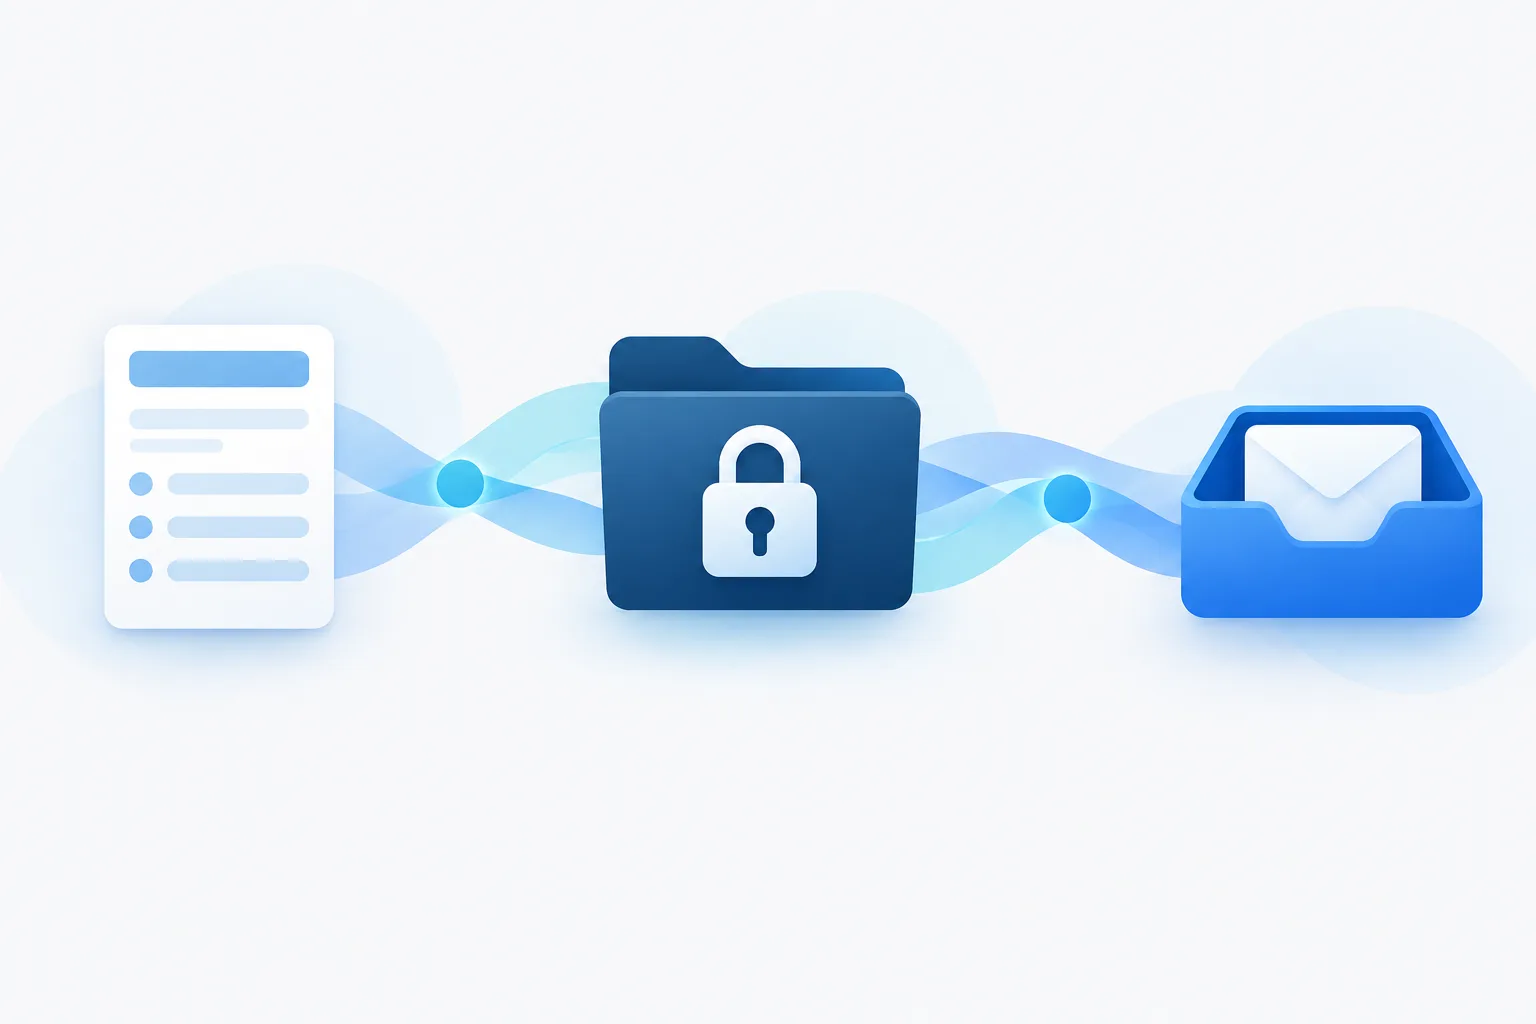
Do not review only what the patient sees on the page. Find out what happens after someone presses submit. Ask the website administrator to map the submission’s path, including:
- Whether the form plugin saves submissions in the WordPress database, and how staff view, export, or delete them.
- Whether information is sent to an email address, and which email service handles delivery.
- Whether the web host, form provider, or another vendor can access or store the submission.
- Whether submissions could appear in site backups, diagnostic logs, spam-filtering tools, or connected services.
- Whether the form sends information to any scheduling, customer-management, or other external system.
A plugin’s privacy statement or compliance label is not a complete review of your actual setup. Configuration matters: a form might store entries even when email notifications are enabled, or a connected service might receive data the practice did not expect to share.
Review vendors and agreements
List the providers involved in receiving, storing, transmitting, or supporting form submissions. This may include the website host, form plugin, email provider, and any connected service. For each, identify what information it handles, where it is processed or stored, and who can access it.
If a provider may handle electronic protected health information on the practice’s behalf, ask the practice’s compliance lead whether a business associate agreement and specific safeguards are appropriate. Confirm the agreement and safeguards for the actual product and configuration being used. A general claim that a product is “HIPAA compliant” does not, by itself, establish that the whole website workflow is suitable.
Hosting is only one part of that workflow. This guide explains why HIPAA-compliant hosting alone does not make a website compliant.
Limit access to submissions
Check which WordPress accounts can view, export, or delete form entries. Access should match staff responsibilities, rather than being available to every account that can log in to the site. Review access when staff duties change, and make sure the practice knows who is responsible for handling requests that come in.
Also consider administrative access outside WordPress. If a submission is delivered to an inbox, check who can access that mailbox and whether messages are forwarded or shared. A secure form can still create unnecessary exposure if its notifications go to a broadly accessible inbox.
Be deliberate about email notifications
Email can be useful for alerting staff that a request arrived, but decide what the notification should contain. Consider sending a minimal alert that directs authorized staff to the approved system, instead of placing sensitive details in the email itself. Confirm the recipient addresses, access to those mailboxes, and what happens if a message is misdirected.
Test the form using non-sensitive sample information. Check the message received, the stored entry, and any connected systems. For related considerations, see email handling for business websites.
Check analytics and third-party tools
Review the appointment page for analytics, advertising, chat, spam-prevention, and other third-party tools. Find out what information each tool receives when a visitor views or submits the form. Check whether form values or sensitive page details could be included in tracking events, URLs, or diagnostic reports.
Ask your website administrator to verify the live configuration rather than relying only on a plugin list. If a tool does not serve a necessary purpose, discuss whether it should be removed from the form page or configured differently. Your privacy lead can determine whether the practice’s disclosures and policies need to address the tools in use.
Set a retention and deletion process
Decide how appointment requests are handled after staff respond. Identify where the practice keeps the information it needs, who decides whether a web submission should be transferred into another record system, and how unneeded copies are removed. Include plugin entries, email messages, exports, and any relevant backups or logs in the review.
Do not choose a retention period by guesswork. Have the practice’s privacy or compliance lead confirm the applicable records policy and how it applies to these submissions. Florida Statutes § 456.057 addresses ownership and control of patient records and disclosure of information; ask the practice’s appropriate advisor how its policies apply to appointment requests and related records (Florida Statutes § 456.057).
Explain what happens after a patient submits
Use plain language to tell people what the form is for and what they should expect. Make clear that sending a request does not necessarily confirm an appointment. State how the practice expects to respond, and give patients an appropriate phone number or other channel for urgent needs. Do not present the form as a way to get emergency assistance.
Before launch, have staff test the complete process: submit a request, confirm it reaches the right person, follow up using the stated workflow, and check that the request is handled and removed or retained according to practice policy. Repeat the review when the form, plugin, host, email setup, or connected services change.
Frequently asked questions
What information should an appointment-request form ask for?
Start with the minimum details scheduling staff need to respond, such as contact information and a preferred time or contact method. Add other fields only after the practice has reviewed why they are needed and how the information will be handled.
Should patients enter symptoms or medical history?
Usually, a scheduling request should not invite detailed clinical information unless the practice has a reviewed reason and appropriate process for collecting it. Consider directing clinical intake to a workflow designed for that purpose.
Where are WordPress form submissions stored?
It depends on the plugin and configuration. Submissions may be stored in WordPress, delivered by email, or passed to connected providers. Check the settings and test the live form to identify the actual data path.
Is it safe to send appointment details in email notifications?
Review what the notification contains, where it is sent, and who can access the mailbox. Consider keeping sensitive details out of the email and using it only to alert authorized staff to check an approved system.
How long should appointment requests be kept?
There is no retention period specified here for every practice and form. Ask the practice’s privacy or compliance lead to apply its records policy, then document how the practice handles submissions and any copies.
Make the form part of a reviewed process
A safer appointment-request form is not just a set of fields. It is a defined process for collecting only what is needed, protecting submissions as they move through the website, limiting access, and following up as promised. The next step is to ask your practice’s privacy lead and WordPress administrator to map the form’s data path together. If you need help reviewing WordPress storage, access, backups, and notification settings, contact Zevonix about website management.